
The U.S. Department of Homeland Security has published notice of an order excluding DeepSeek products from federal civilian procurements and requiring removal of all DeepSeek and DeepSeek-affiliate products, and third-party products and services developed using DeepSeek implementations from civilian agency information technology. The Federal Register public inspection notice (Doc. 2026-21447, Docket DHS-2026-0628) was filed on October 19, 2026, at 8:45 a.m., with a scheduled publication date of October 20, 2026.
The signed appendix is Exclusion and Removal Order #2026-01 under the Federal Acquisition Supply Chain Security Act (FASCSA), with an original release date of July 24, 2026 on the order itself. It is signed by Markwayne Mullin, Secretary of Homeland Security, with Russell Vought, Director of the Office of Management and Budget, copied. The Federal Register notice is signed by James H. Percival II, General Counsel, DHS. Contact for the FASCSA Order Implementation Team is fascsa.orders@cisa.dhs.gov at CISA's Cybersecurity Division.
What the order requires
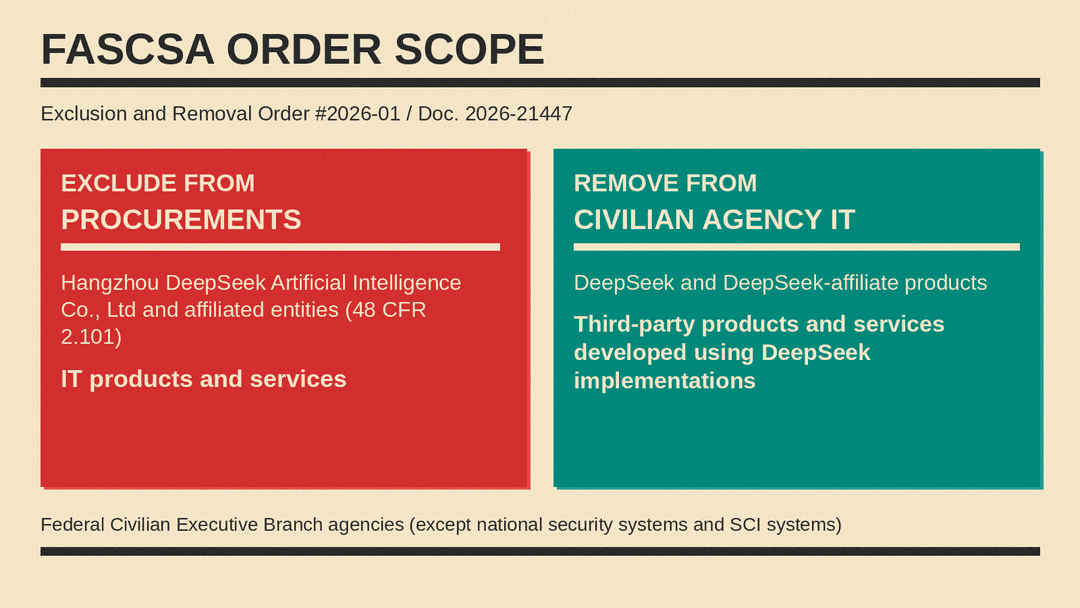
The notice summary states that the Secretary ordered two actions:
- Exclusion of information technology products and services developed by Hangzhou DeepSeek Artificial Intelligence Co., Ltd (DeepSeek), including affiliated entities as defined in applicable regulations and 48 CFR 2.101, from federal civilian agency procurements.
- Removal of all DeepSeek and DeepSeek-affiliate products, and third-party products and services developed using DeepSeek implementations, from civilian agency information technology.
Authority is the Federal Acquisition Supply Chain Security Act of 2018, 41 U.S.C. 1321-1328, and implementing regulations at 41 CFR 201-1, following a Federal Acquisition Security Council recommendation.
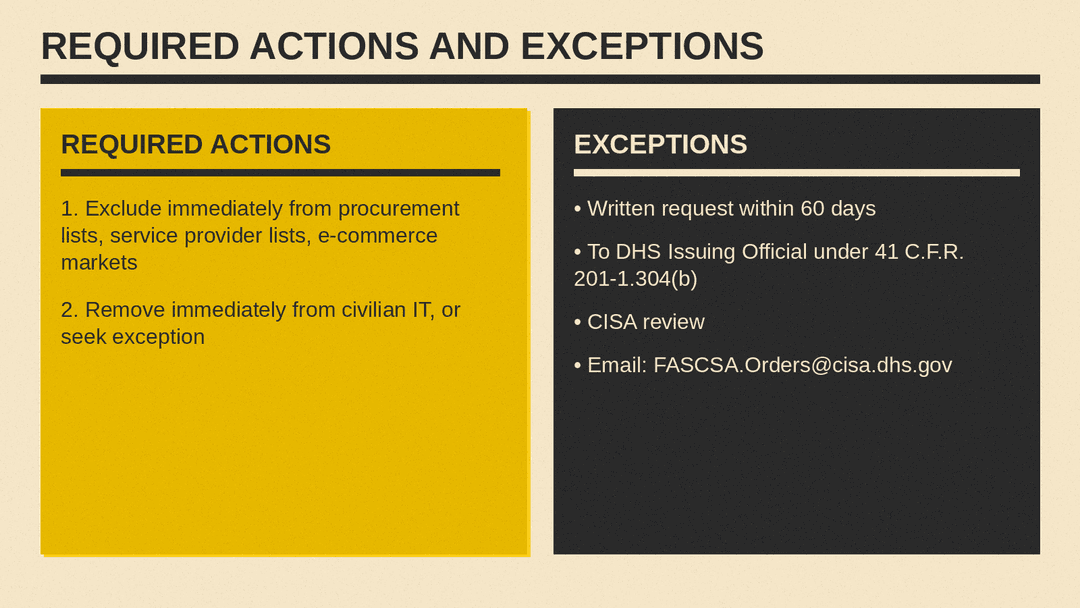
The order applies to Federal Civilian Executive Branch agencies, except for their national security systems and secure compartmented information systems. Required actions in the appendix tell agencies to exclude DeepSeek and affiliates from procurement lists, service provider equipment lists, e-commerce markets, and similar channels immediately, and to remove covered products from civilian IT immediately or seek an exception.
Risk findings in the order
The appendix describes DeepSeek as a foreign, privately owned company in the People's Republic of China, with servers in the PRC, and states that its models pose multiple threat vectors. It raises concern that use through a prompt-and-response process may transfer sensitive data to the PRC if used by U.S. government employees or vendors.
Reuters (David Shepardson, Oct. 19, also carried by CNA) confirms the removal and acquisition ban and quotes DHS language that DeepSeek models pose "multiple threat vectors" and that use "may result in the transfer of sensitive data to the PRC if used by U.S. government employees or vendors."
Bloomberg Law (Michael Shepard, Oct. 19) reports that the Trump administration barred civilian U.S. government agencies from using DeepSeek products or services, that agencies must remove DeepSeek products, that the order cites U.S. cybersecurity laws, and that the Chinese firm is barred from federal government contracts.
Exceptions and compliance
Agencies may request an exception in writing within 60 days of the order's issuance to the DHS Issuing Official under 41 C.F.R. § 201-1.304(b). Requests must identify the order, the exception sought, the covered article or product, a compelling justification, and alternative mitigations. CISA reviews requests. The appendix points agencies to FASCSA.Orders@cisa.dhs.gov.
The appendix also directs interim steps while removal is underway, including monitoring traffic, logging and controls on data exfiltration, and flagging anomalous activity. CISA may provide technical assistance to agencies that lack internal capacity. DHS is to approve or disapprove exception requests in writing. The Secretary is to review the order within one year and annually thereafter, as FASCSA requires.
Context
This is a FASCSA exclusion and removal order published for public inspection on October 19, 2026. In August, we covered New York Times reporting that the White House had weighed wider limits on Chinese open models, including which models federal agencies could use, before backing off. DeepSeek continues to ship open-weight models into commercial channels, including the recent V4.1-Flash-1017 update. Separately, China has floated export controls on frontier AI models, agents, and chip design. Those tracks address different instruments and audiences. The DHS order's immediate effect is on U.S. federal civilian procurement lists and agency IT inventories, plus third-party services built on DeepSeek implementations used by those agencies.
Sources
- Federal Register public inspection: Order exclusion and removal of DeepSeek products (Doc. 2026-21447)
- StreetInsider / Reuters: US banning Chinese AI DeepSeek from government agency IT systems (David Shepardson)
- CNA: US banning Chinese AI DeepSeek from government agency IT systems
- Bloomberg Law: US Moves to Bar DeepSeek From Federal Agencies and Contracts (Michael Shepard)
