
Anomaly Innovations, the developer behind the open-source AI coding tool OpenCode, confirmed that a security breach exposed third-party API credentials stored by approximately 1.4% of its Console users. The unauthorized access targeted an internal legacy system during decommissioning and was leveraged to execute automated model distillation attacks against frontier AI providers.
Update, Oct 19
The exposed keys are the ones users saved in OpenCode Console, the company's optional hosted service. The OpenCode command-line and desktop apps keep provider keys added on the machine in a SQLite database there, The Hacker News reports. Co-founder Dax Raad wrote on X that the breach involves "the OpenCode Console, not OpenCode itself," and that those keys "never come to us."
Users say they have paid for usage they did not run. Dealroom reported that Colin Parsons wrote on X that his OpenAI key was "pounded" for $281 and his Anthropic key for $168, and that Preston Zeller put his losses at $1,700. Notebookcheck reported that one Reddit user saw $400 in unauthorized charges on an Anthropic account, and another said Google usage charges had reached around €200 and their project had been suspended for excessive abuse. These are the users' own accounts. The Hacker News notes that OpenCode's wording is that the keys "may have been exposed," and that it has not said any key was copied or used.
The attacks did not stop at the breach. On October 18, Raad wrote on X that attackers had been "non stop trying to attack our systems for the past 48 hours," and that "a side effect is everything is getting hardened," according to The Hacker News.
A provider key is a bearer credential. Deleting the key from Console does not revoke it, and a Console budget cannot cap that use either, because Console only sees requests that pass through its own gateway. For a key that was saved in a Console workspace, The Hacker News lists these steps from OpenCode's email and the providers' own guidance:
- Revoke the key in the provider's own dashboard and create a new one, following the instructions from OpenAI, Anthropic, or Google.
- Update every application and script that used the old key.
- Review usage and billing at the provider for requests you did not make, going back at least to October 16. OpenCode has not said when the unauthorized access began.
- Set a spend limit or alert at the provider and give each tool its own key, so a copied key does less damage and its use is easier to trace.
Legacy Infrastructure Exposure
OpenCode allows developers to connect external AI services by providing their own API keys for model providers such as Anthropic, OpenAI, and Google. According to disclosures sent to affected users, threat actors gained access to an older server environment slated for retirement where workspace configurations and linked credentials remained accessible.
The company stated that the breach was restricted to a subset of users with external provider integrations active on OpenCode Console. Accounts without linked third-party keys were unaffected.
Automated Distillation and API Depletion
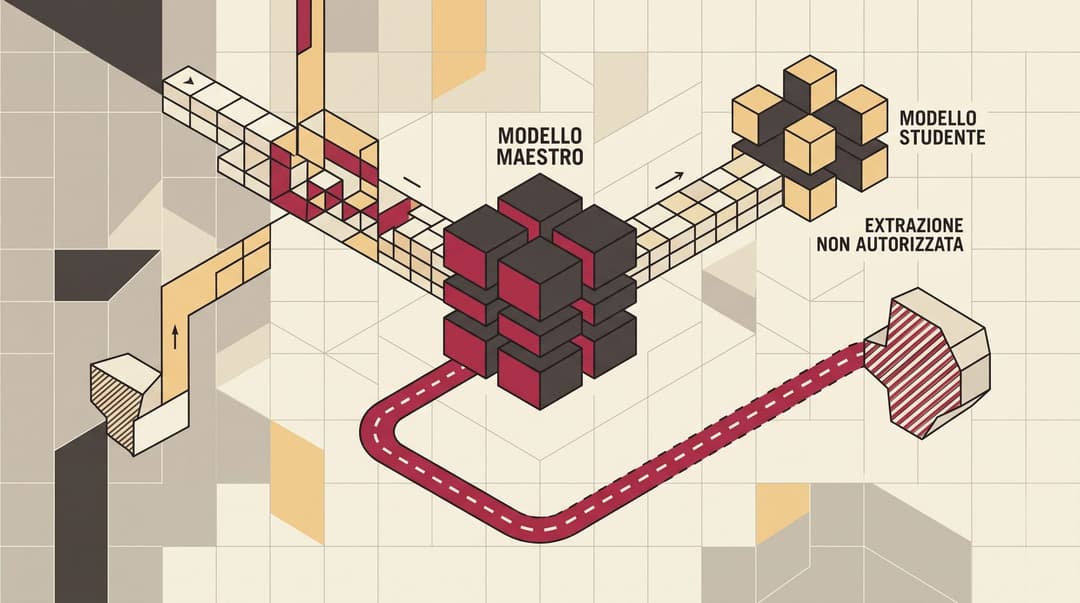
Exposed API keys were quickly repurposed to run high-throughput queries against upstream model endpoints. Model distillation involves systematically querying frontier models to generate synthetic dataset outputs for training downstream or localized models.
Multiple developers reported sudden surges in unauthorized consumption before notifications were delivered. Documented unauthorized usage included:
- A Reddit user reported about $400 in unauthorized charges on an Anthropic account, according to Notebookcheck.
- Preston Zeller put his total losses at $1,700, according to Dealroom.
- Another user reported about €200 in Google usage charges and said their project was suspended for excessive abuse, according to Notebookcheck.
In addition to billing spikes, secondary disruption occurred across OpenCode authentication systems. Several users experienced expired session tokens and failures with social login providers during key revocation efforts.
Remediation and Risk Mitigation
OpenCode advised all impacted Console users to immediately revoke and rotate their API keys across Anthropic, OpenAI, and Google developer dashboards. The company confirmed it is coordinating directly with the affected AI providers to trace unauthorized traffic patterns and mitigate further impact.
The incident underscores the operational risk of storing unsegmented third-party API keys within hosted developer platforms. As distillation defenses increase across direct API endpoints, third-party tooling platforms holding persistent user credentials present high-value vectors for automated extraction.
Sources
- OpenCode Security Update on X
- Notebookcheck: OpenCode hacked, users urged to revoke their API keys
- Community Incident Reports on Reddit
- The Hacker News: OpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API Keys
- Dealroom: OpenCode breach drains users' AI keys as platforms holding customer credentials come under attack
