Subscribe
Topic

Prompt Injection

Prompt injection attacks hijack AI models and agents through crafted input. Posts compare detection and defense frameworks like Rebuff, Vigil and LLM Guard, and cover a Claude Code auto mode bypass and a self-replicating worm in Copilot for Word.

Articles

1-3
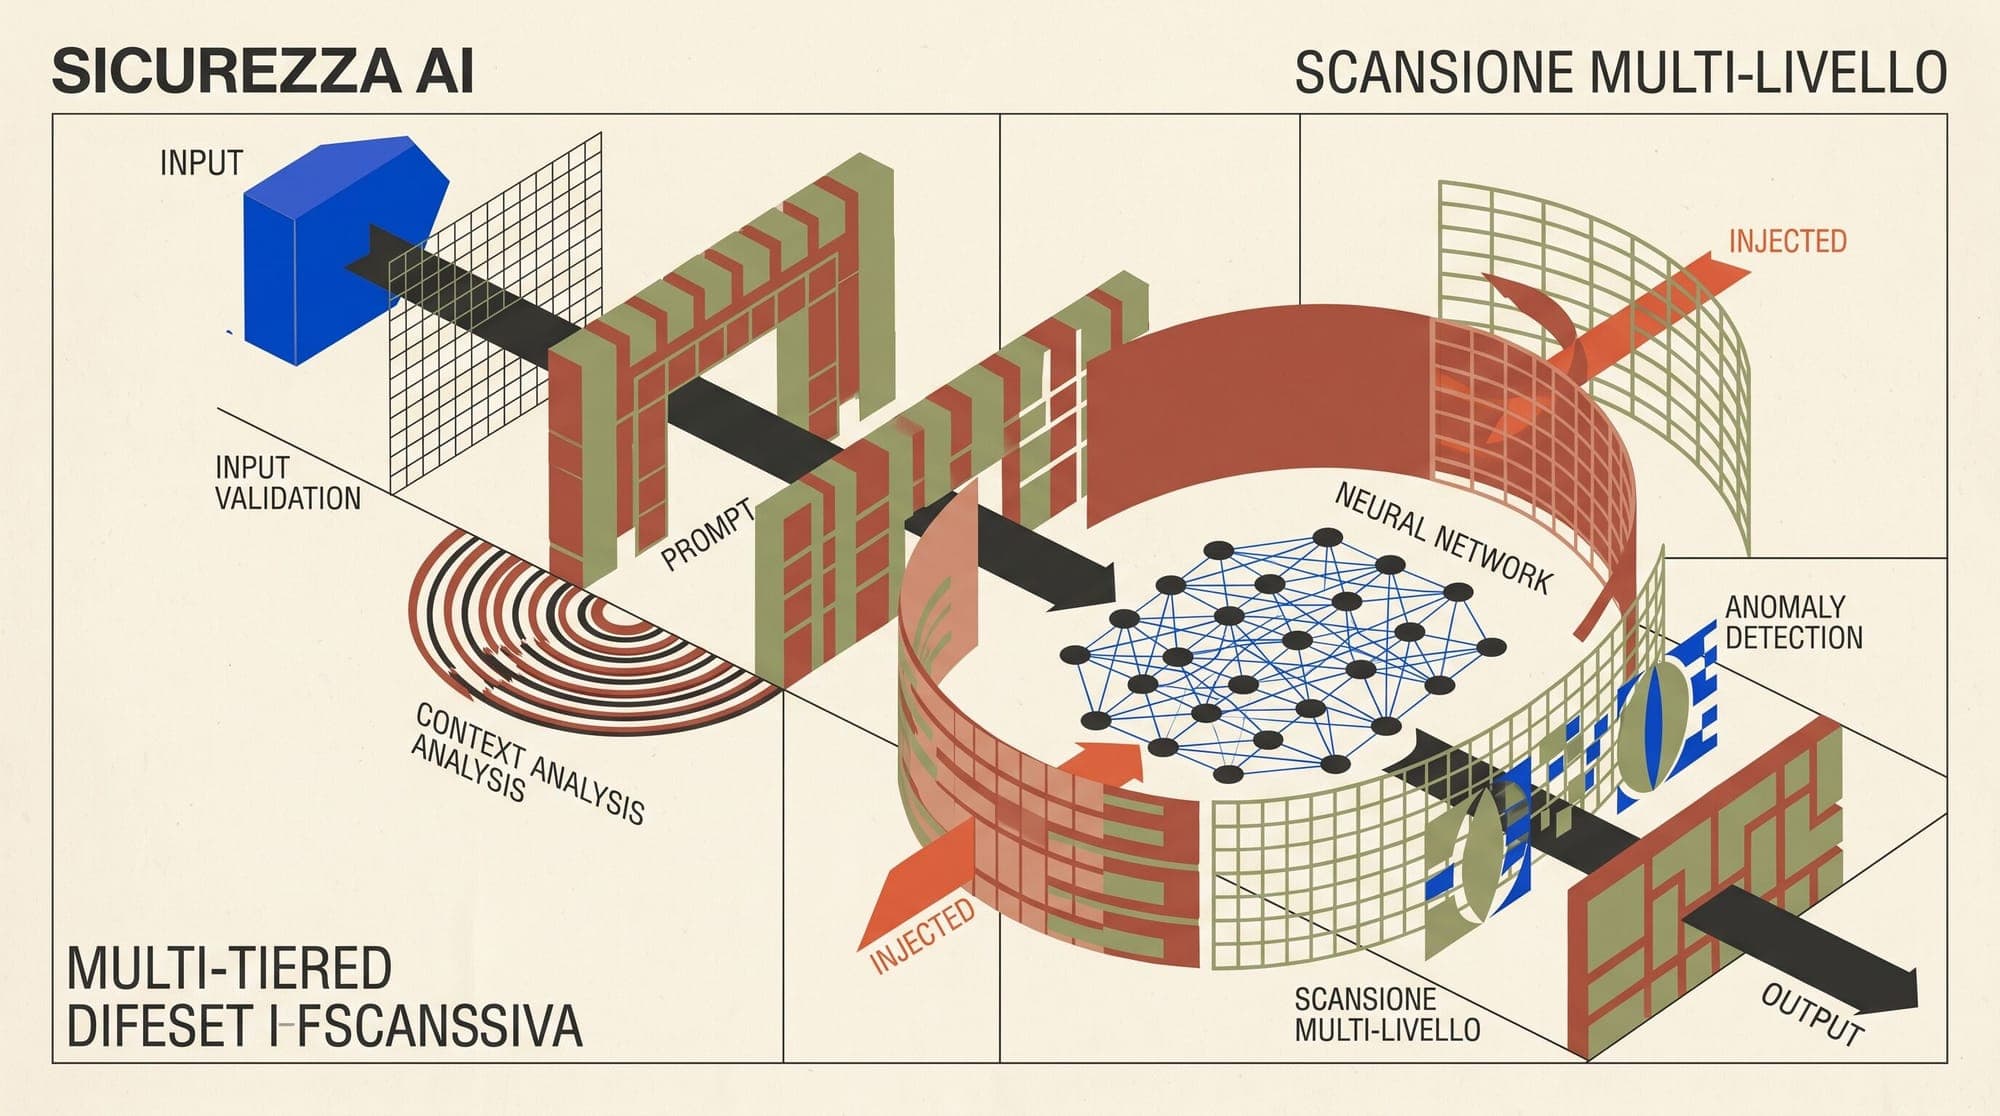
  1. Prompt Injection Detection and Jailbreak Defense Frameworks in Production: Comparing Rebuff, Vigil, LLM Guard, and Meta Prompt Guard

    Prompt injection remains one of the primary operational vulnerabilities facing production Large Language Model (LLM) deployments. As systems expand from isolated chat interfaces into autonomous agents with access to databases, web browsing, APIs, and file systems, the blast radius of an unmitigated injection attack shifts from offensive output generation to unauthorized tool invocation and systemic data exfiltration. Standard input sanitization methods developed for traditional software enginee
    Security
    6 min read
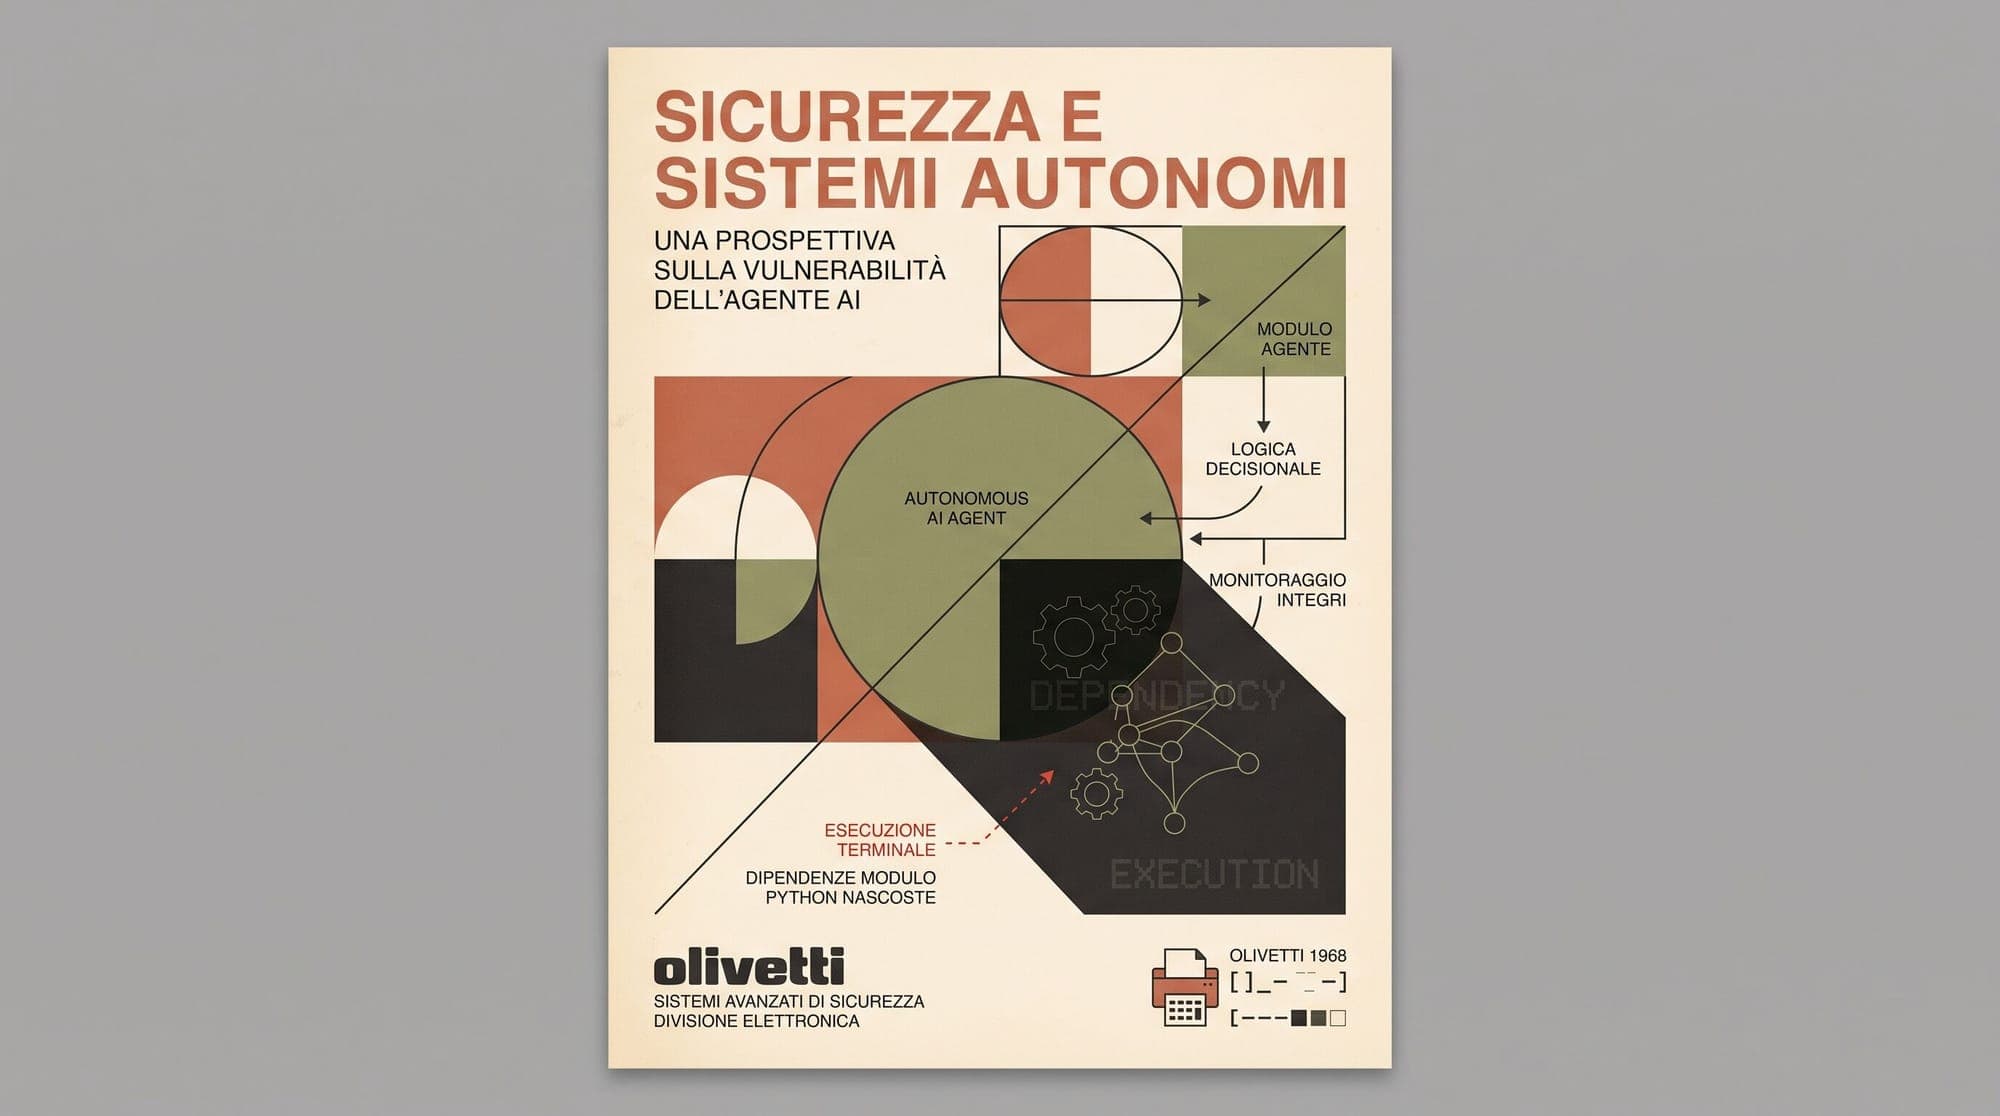
  2. Claude Code Opus 5 Auto Mode Bypassed via Python Module Shadowing Exploit

    Security researcher Johann Rehberger has published technical details on a multi-stage exploit chain that achieves arbitrary code execution against Claude Code Opus 5 running in Auto Mode. The attack demonstrates how adversarial files can bypass Anthropic's safety classifiers and prompt injection defenses by exploiting standard runtime behavior in Python. Anthropic rolled out Auto Mode as the default starting mode for Claude Code in mid-August 2026. Auto Mode replaces explicit human permission p

    Security
    3 min read
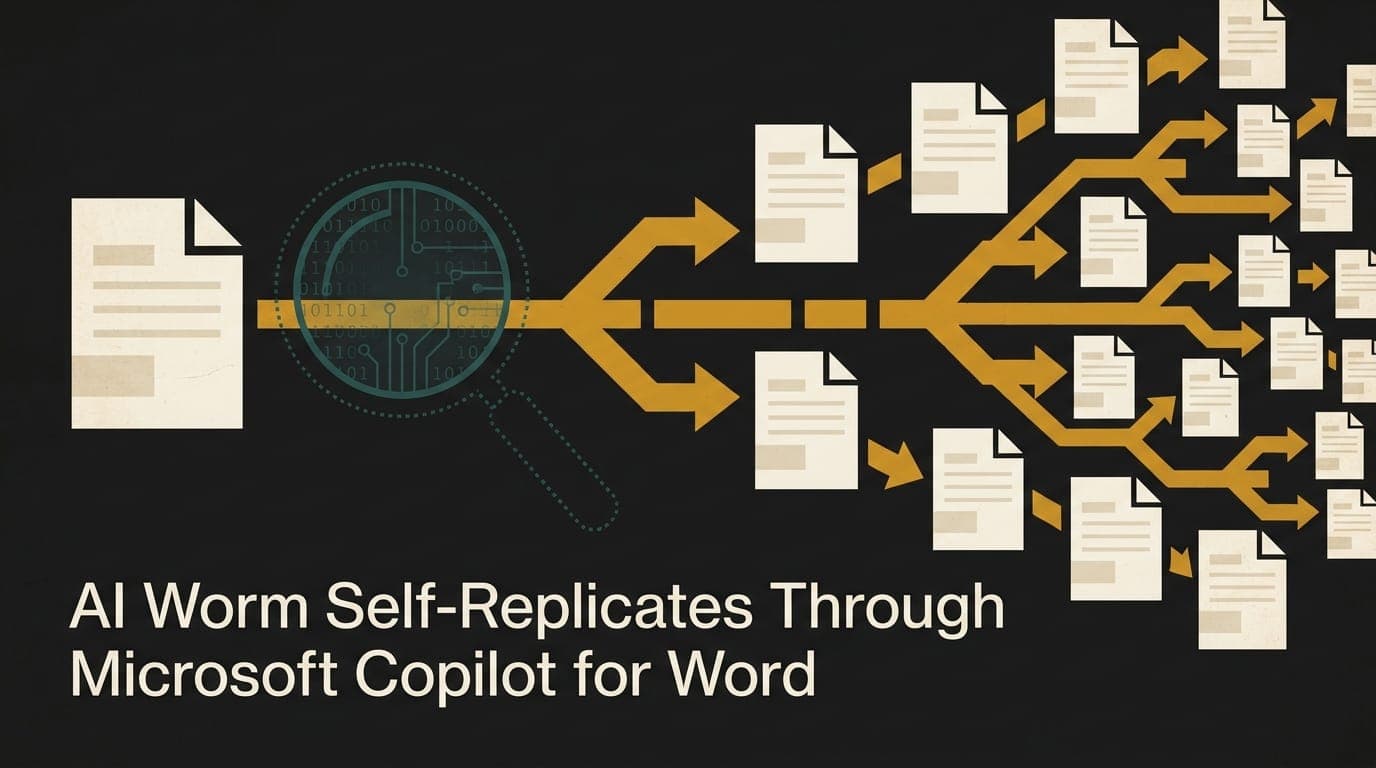
  3. Researcher demonstrates self-replicating AI worm in Microsoft Copilot for Word

    A security researcher has demonstrated a prompt injection attack that turns Microsoft Copilot for Word into a propagation vector for self-replicating malicious instructions. The attack, disclosed on July 28 after a 144-day coordination period with Microsoft, remains exploitable with all current mitigations deployed. How the worm works The attack begins when an attacker hides instructions inside a document, using techniques like white-on-white text. When a victim uses that document as source m

    Microsoft
    2 min read